ChatGPT now shows a trail of account security events
A new Security history view lists recent sign-ins and changes to protections such as passkeys. OpenAI says location and device details may be approximate or missing.
OddBrief EditorialAI-assisted, human-reviewed
 Internet
Key facts
- Fact 1
- OpenAI added Security history on September 25
- Fact 2
- It includes sign-ins, sign-outs and protection-setting changes
- Fact 3
- The view is under Settings, Security and login on the web
- Fact 4
- Location and device details may be approximate or unavailable
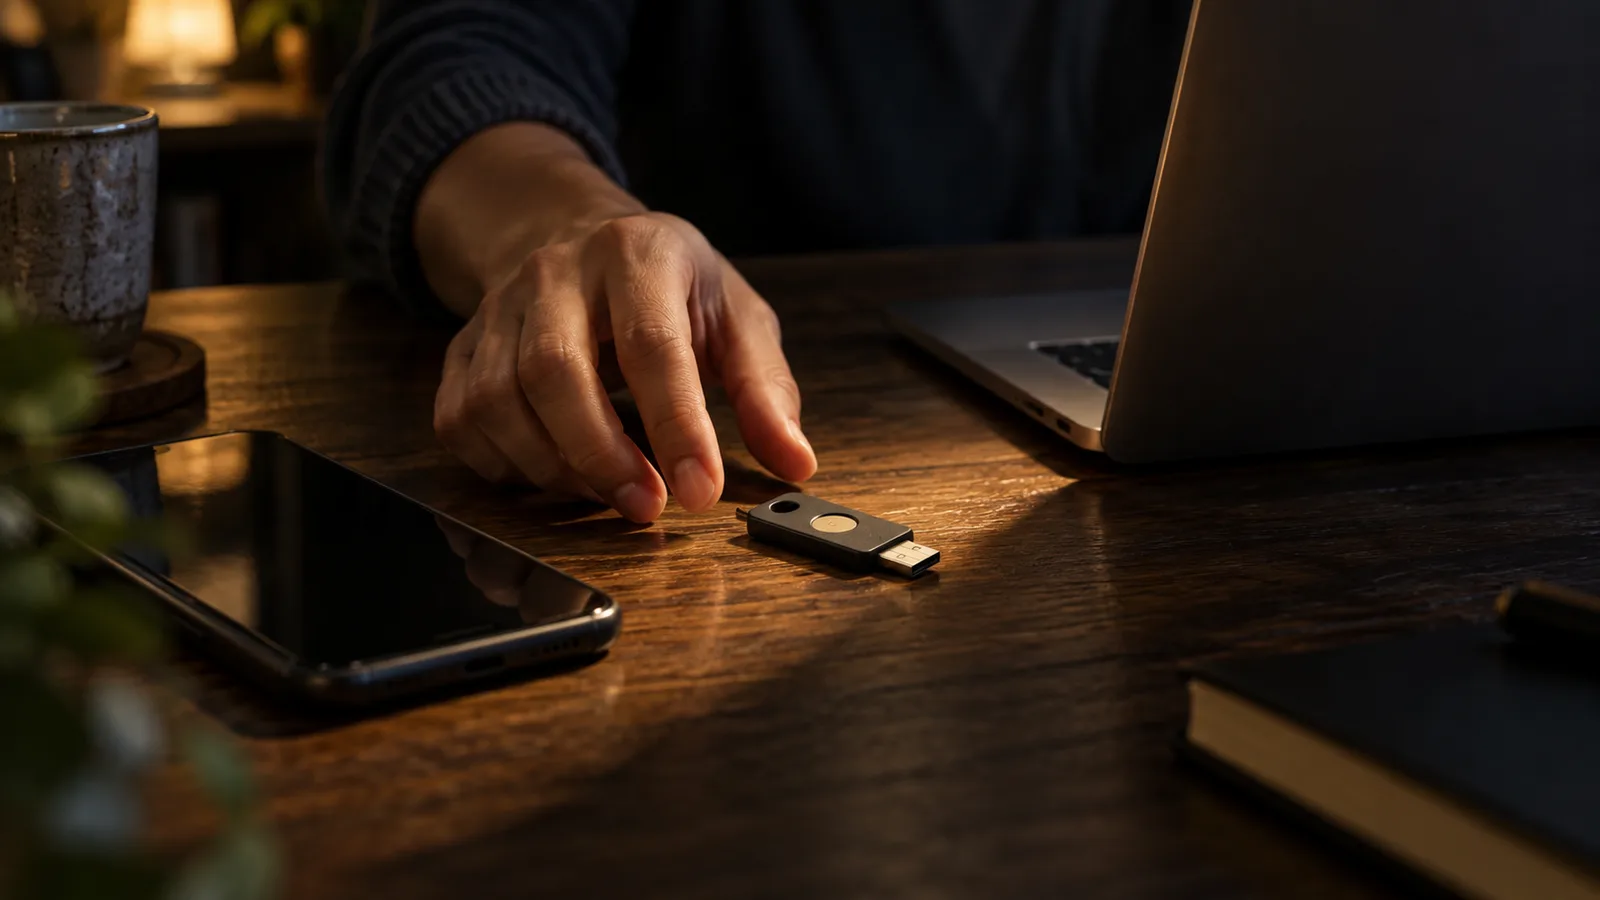
OpenAI added Security history to ChatGPT on September 25. The feature gives account holders a place to review recent security activity, including sign-ins, sign-outs and changes to multi-factor authentication, passkeys and other security settings. It sits under Settings, then Security and login, on the web.
The events behind an account
An unfamiliar login notification can be hard to assess if it arrives in isolation. A timeline lets a user compare the event with password changes, security setting changes and other sessions. OpenAI says entries show the time, location and device when those details are available. It also warns that some information may be approximate or unavailable, so a city or device label should not be treated as a perfect forensic record.
The supporting account-security guide tells users to review Security history and Active sessions separately. The former records past events; the latter shows current sessions that can be managed. Someone who sees activity they did not authorize can follow the guide's response steps, including securing the account and signing out of sessions. That distinction matters because reading a history does not itself end an unwanted session.
OpenAI has not said in the release notes how far back the history extends, whether every kind of suspicious event is captured, or whether all accounts will see identical detail. The announcement also does not claim that the feature prevents account compromise. Its value is visibility: a person can notice a change that otherwise might pass without explanation.
A useful record with limits
The obvious use case is a routine check after a new-device login or an unexpected security email. But location data can be misleading when people use mobile networks, travel or route traffic through privacy tools. An unfamiliar location deserves investigation, not an automatic conclusion that an attacker entered the account.
The feature is part of a larger shift toward giving users a readable account audit trail. That is particularly relevant when an account connects documents, work apps and other services, because one compromised login can affect more than a chat history. OpenAI's own instructions emphasize responding to activity a person cannot explain, rather than relying on the timeline alone as a security guarantee.
Security history is available through the web settings described in OpenAI's September 25 notes. The company has not supplied evidence yet about whether the view reduces unauthorized access or how often it helps users identify it. For now, it offers a clearer answer to a basic question: what happened in this account recently?
Sources
- ChatGPT release notesOpenAIprimary source